What is CVEngine?
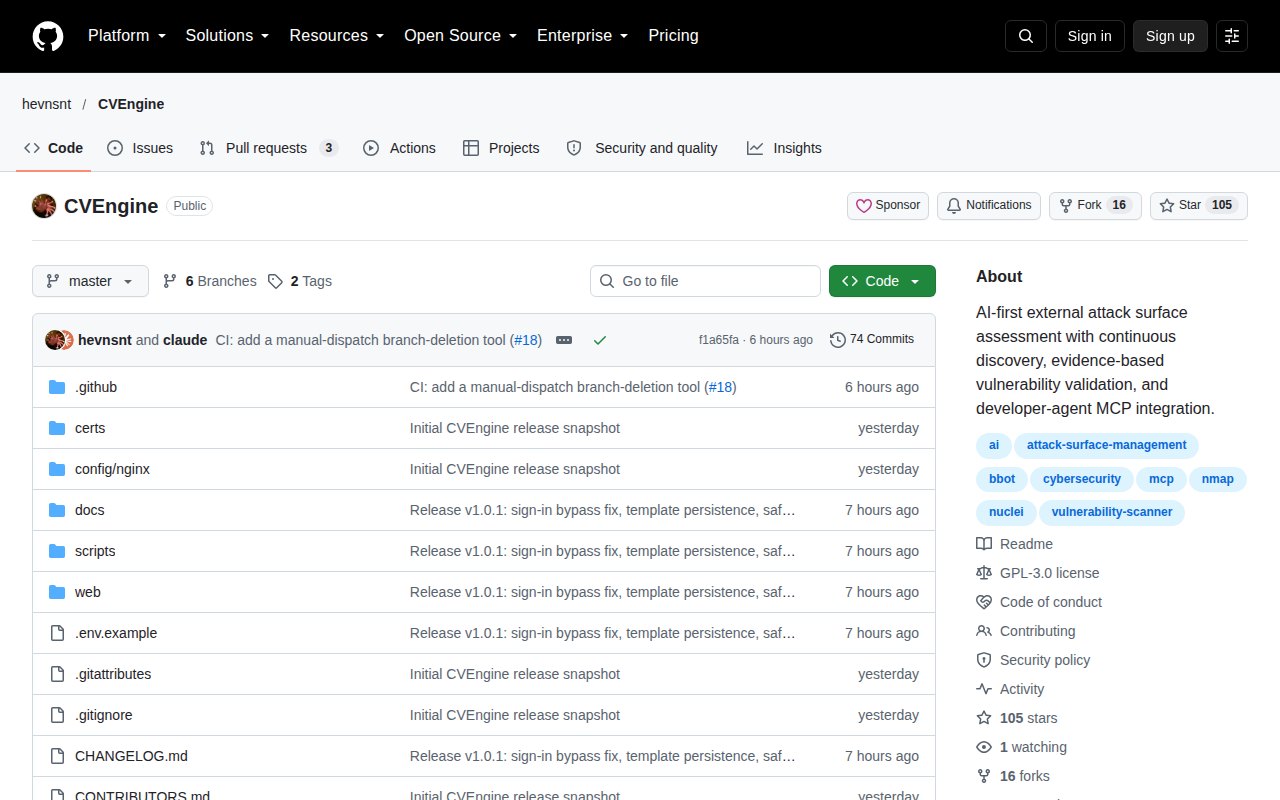
CVEngine is a tool designed for external attack surface assessment. It utilizes AI-first methodologies to perform continuous discovery of assets. The system focuses on evidence-based vulnerability validation and includes support for developer-agent MCP integration.
Key Features
- Continuous Discovery: The tool performs ongoing external attack surface assessment to identify assets.
- Evidence-Based Validation: Vulnerabilities are validated using evidence-based methods rather than heuristic assumptions.
- Developer-Agent MCP: Includes support for Model Context Protocol (MCP) integration for developer agents.
Pricing
Public / open project materials as listed on the official site or repository; confirm license and any paid packaging there before relying on this page.
Limitations
- External Scope Only: The tool is specifically designed for external attack surface assessment, not internal network penetration testing.
- AI-First Dependency: Core functionality relies on AI-first assessment processes, which may require specific model configurations or API access.
Who is it for?
Security engineers and developers who need to automate external attack surface discovery and vulnerability validation. It is suitable for teams integrating AI-driven security checks into their development workflows via MCP.
Alternatives
- security-audit-skill — Coding-agent security audit skill
- Claude-Red — Offensive security skills for Claude
- OpenShell — Isolated runtime for autonomous agents
No comments yet. Be the first to share.